
Best for hourly automated testing
Vanta
The only alternative here with hourly default tests, plus 400+ integrations.
- Integrations
- G2 rating
- 4.6 · 2,732 reviewsUser reviews[3]
Compliance platform alternatives
Filter by what you need. The table and the profiles below update together.
| Best for | Reason to compare | Frameworks | Profile | |||||
|---|---|---|---|---|---|---|---|---|
| Growth-stage SaaS teams that expect to add frameworks and want configurable tests | Most auditors in the directory; custom tests | $9,415[4] to $68,250 |
4.7 (1,397) | 30+[12] |
300+[16] |
50 directory firms[6] |
Full profile ↓ | |
| Cloud-native SaaS teams on mainstream stacks that want broad, prebuilt coverage | Largest published integration catalogue | $7,500[4] to $57,221 |
4.6 (2,732) | 35+[11] |
400+[11] |
41 directory firms[6] |
Full profile ↓ | |
| Engineering-led teams that value inspectable code or the option to self-host | Inspectable code, a self-hosting option and 580+ integrations | 4.7 (74)Small sample | 580+[15] |
Full profile ↓ | ||||
| Early- to growth-stage SaaS teams seeking guided first-audit preparation | 300+ integrations and 45 directory auditors | $13,167[4] to $16,000 |
4.7 (1,684) | 25+ automated[13] |
300+[13] |
45 directory firms[6] |
Full profile ↓ | |
| Established GRC teams running several frameworks and audits at once | Built for concurrent multi-framework audits | $22,215[4] to $70,000 |
4.5 (222) | Full profile ↓ | ||||
| Growth-stage tech teams managing SOC 2 alongside other frameworks | Highest G2 rating on this page | $15,000[7] "from" price |
4.9 (1,325) | Full profile ↓ | ||||
| Teams that want expert guidance on clearly named packages | Published $7,500 entry package and 300+ integrations | $7,733[4] to $32,575 |
4.7 (829) | 300+[14] |
13 directory firms[6] |
Full profile ↓ | ||
| Teams wanting software and a connected audit process from the same provider | Audit from a related CPA firm | $8,700[7] "from" price |
4.7 (585) | Own CPA firm[5] |
Full profile ↓ | |||
∅ No alternative matches every filter. Remove one, or . Products with undisclosed data never match a filter that needs it. | ||||||||
● vendor-reported · ○ third-party · ◐ user reviews · ≈ our estimate · ∅ not disclosed. Numbers in brackets link to sources.
How this list is ordered By how many of the switching reasons above each product addresses, using the criterion stated under each reason, then alphabetically. Numbers are list positions, not scores.
The short answer
Teams usually look beyond Scytale over integration reliability, add-on costs or auditor fit. Drata, Vanta, Sprinto and Secureframe publish larger integration catalogues, and Drata, Sprinto and Vanta have the most auditors working in them. Thoropass runs the audit itself. Comp AI suits teams that want to inspect or self-host. Scytale still fits a first SOC 2 without a compliance lead.
Where Scytale stands today
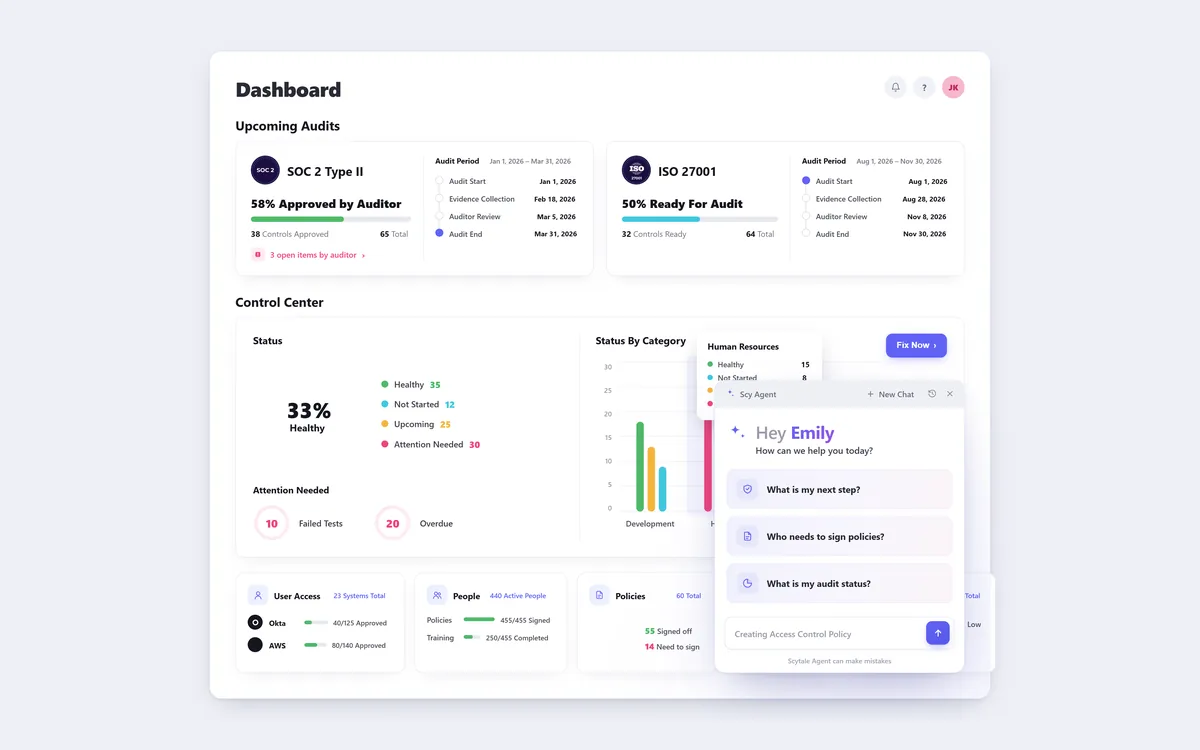
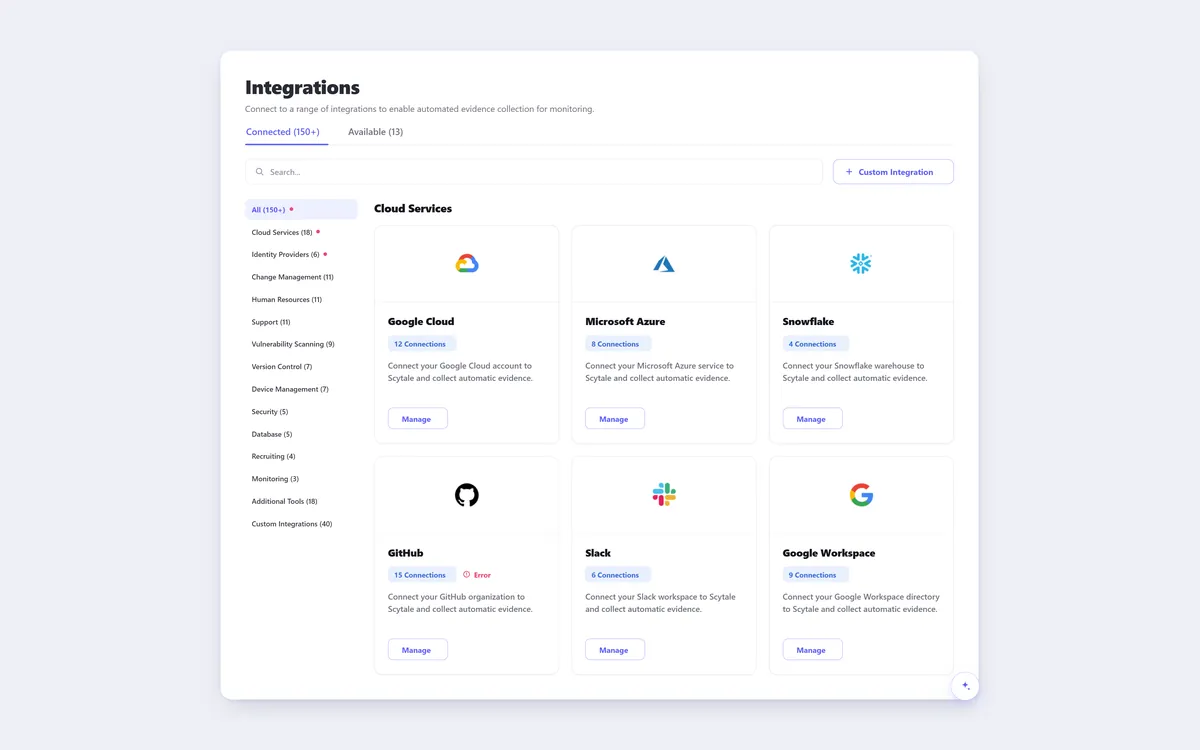
5 reasons recur across reviews and independent assessments. Find yours, then jump to the alternatives that address it.
Reviews quoted by a competitor and a listing site describe integrations that don't work as expected when infrastructure doesn't match Scytale's expected setup, unreliable AWS control population, and occasional bugs. Scytale publishes 150+ integrations.
Counts as addressed when: Publishes a larger integration catalogue than Scytale's 150+.
The $7,500 starting price covers the platform and one framework. On its AWS Marketplace listing, each extra framework starts at $2,100, framework consulting at $4,000, penetration testing at $4,500, security questionnaires at $12,000 and a virtual GRC expert at $36,000.
Counts as addressed when: Publishes a lower all-in price for the same scope.
No attestation firm in SOC2Auditors' directory lists Scytale as a platform it works with. Scytale sells a separate third-party audit service from $4,200.
Counts as addressed when: Listed by 25 or more firms in the same directory, or the provider runs the audit itself.
Scytale's packages pair the platform with consultants. Teams with in-house compliance capacity, or unusual setups, are a weaker fit.
Counts as addressed when: Positioned for self-serve teams, with custom tests or inspectable code.
Scytale is described as best for a first SOC 2 without a GRC lead. Teams running several frameworks and audits at once look for tools built for that.
Counts as addressed when: Positioned for multi-framework or established GRC programmes.
Switching mid-programme has real costs. Staying is often the right call if any of these apply.
Get the add-ons you'll need (extra frameworks, questionnaires) priced into the renewal, then ask one alternative for a quote on exactly the same scope. Scytale publishes per-item starting prices on AWS Marketplace, which makes that comparison straightforward. [1]
Four common situations and the alternative that fits each. These are fit labels, not rankings.
Best for hourly automated testing
The only alternative here with hourly default tests, plus 400+ integrations.
Best if your auditor already uses a platform
Listed by 50 audit firms in an independent directory, the most of any product here.
Best with the audit from the same provider
Platform and audit come from Thoropass and its related CPA firm.
Best for inspectable code or self-hosting
AGPLv3 open core you can inspect, and a documented self-hosting option.
Each alternative gets the same profile: who it fits, the data, how it differs from Scytale, and what switching involves.
·
Compliance automation platform with custom tests, compliance checks in infrastructure code and a dedicated auditor portal.
Compliance automation platform with the largest published integration catalogue and hourly automated tests.
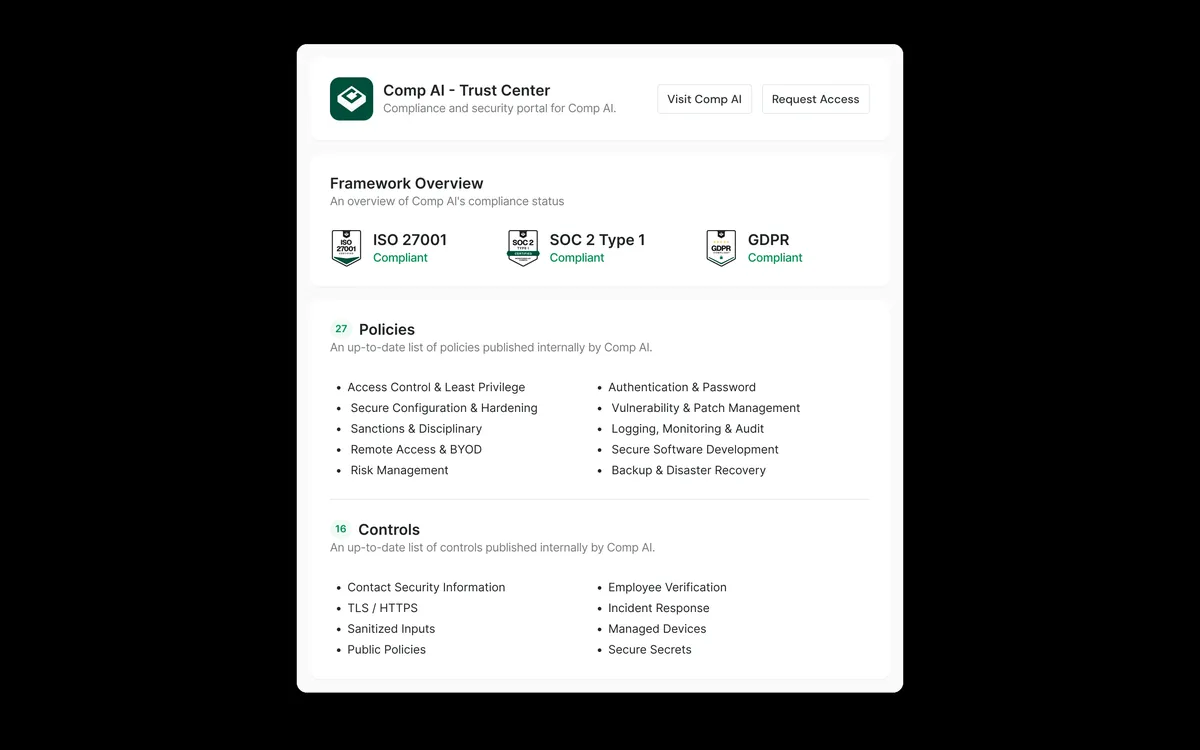
Open-core compliance platform whose evidence-collection code can be inspected or self-hosted, with a managed cloud option.
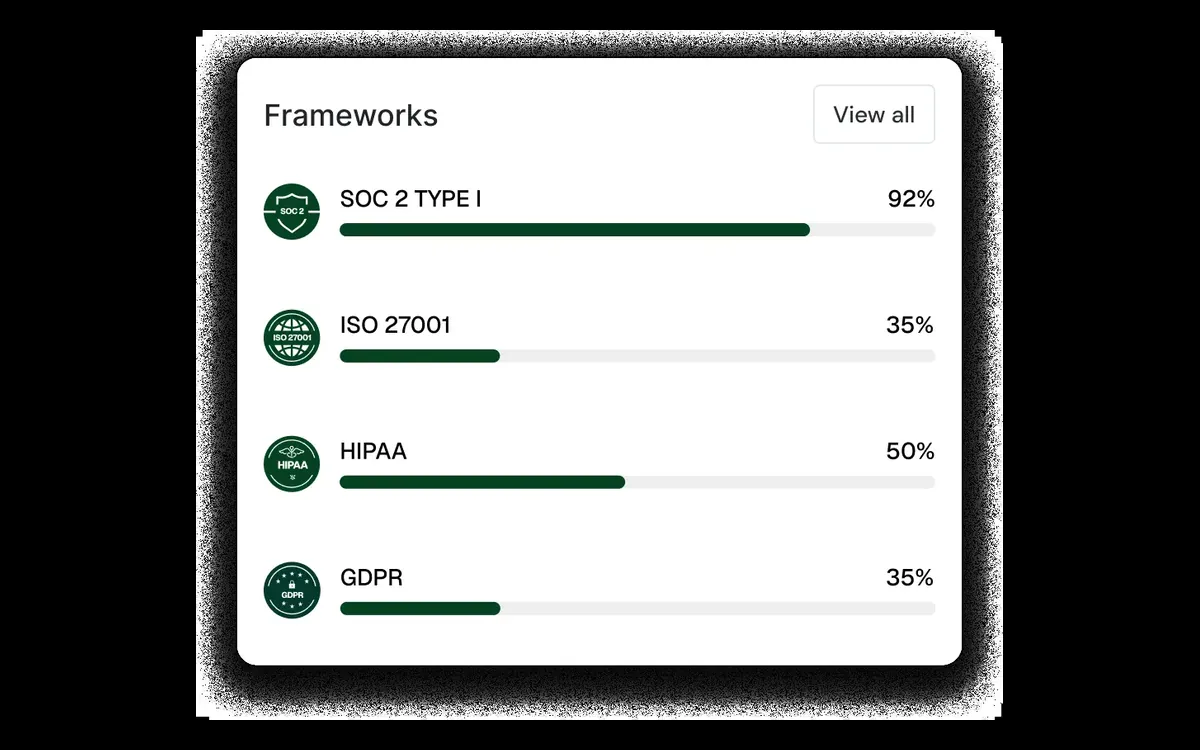
Compliance automation platform focused on guided first-audit preparation for SaaS teams.
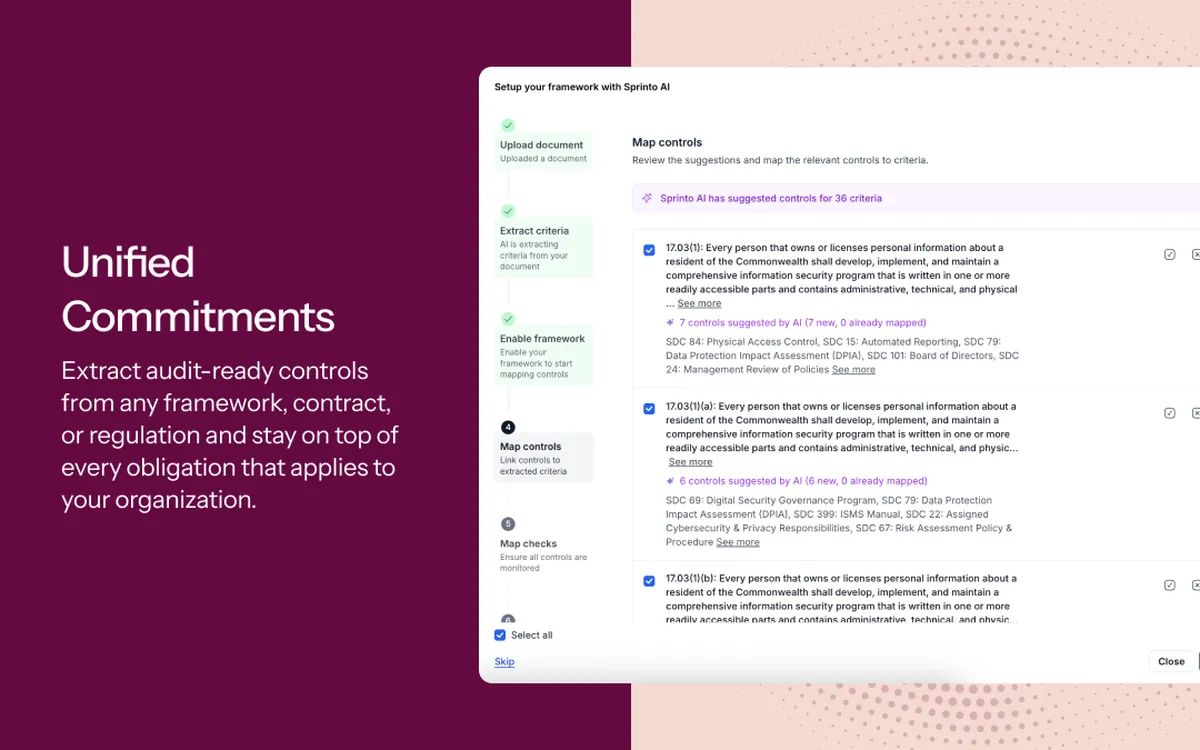
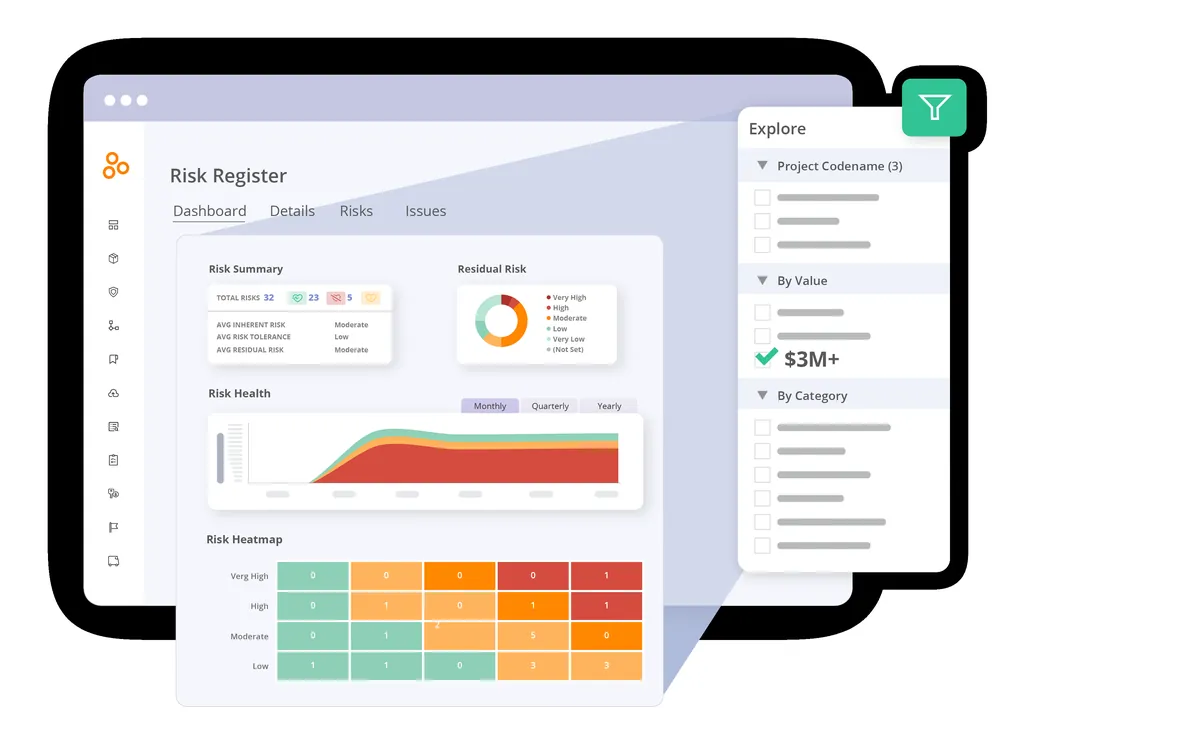
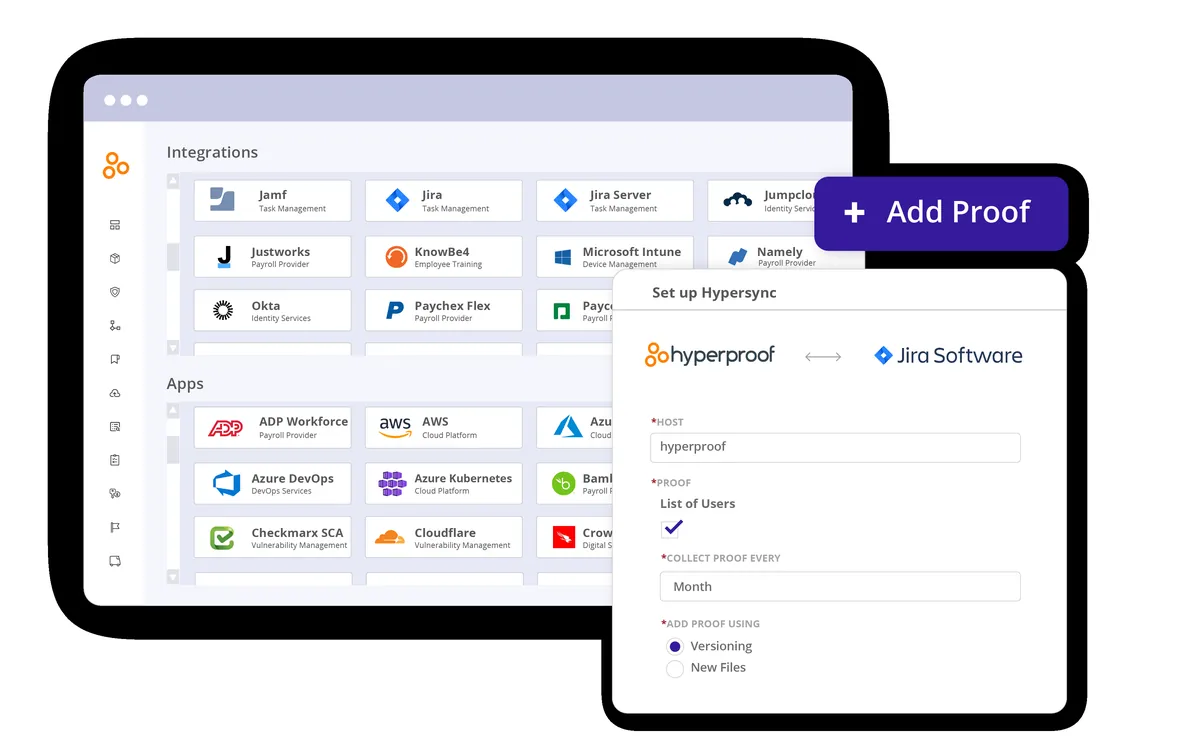
Governance, risk and compliance platform for established teams running several frameworks and audits at once.
Compliance and risk platform for growth-stage tech teams running SOC 2 alongside other frameworks.
Compliance platform sold as named packages (Fundamentals, Complete, Defense) with expert guidance.
Compliance platform paired with its related CPA firm, Thoropass Assurance, so software and audit come from one provider.
No profiles match the current filters.
On published figures, none is clearly cheaper. Scytale's AWS Marketplace floor is $7,500 a year for the platform and one framework, and Secureframe's Fundamentals package also starts at $7,500. Thoropass's platform starts at $8,700 before its audit. On observed contracts, Sprinto has the lowest median here ($15,000 on Vendr), then Vanta and Secureframe ($20,000). Compare quotes for the same scope.
Annual platform subscription on one scale, Scytale first as the baseline. Ranges are observed contracts (Vendr); a fading bar is a published "from" price; the black tick is a median; hatching means no price is published.
Scytale is the shaded baseline column. Tick the alternatives you're weighing, then compare only those.
| Capability | ScytaleBaseline | Drata | Vanta | Comp AI | Sprinto | Hyperproof | Scrut Automation | Secureframe | Thoropass |
|---|---|---|---|---|---|---|---|---|---|
| SOC 2 | Included | Included | Included | Included | Included | Included | Included | Included | Included |
| ISO 27001 | Included | Included | Included | Included | Included | Included | Included | Included | Included |
| HIPAA | Included | Included | Included | Included | Included | Not disclosed | Included | Included | Included |
| Auditor workspace | Included | Included | Included | Partial | Included | Included | Included | Included | Included |
| Trust centre | Included | Included | Included | Included | Included | Partial | Included | Included | Included |
| SCIM provisioning | Included | Add-on or higher tier | Add-on or higher tier | Not disclosed | Not disclosed | Included | Included | Add-on or higher tier | Included |
| Audit from the same provider | Add-on or higher tier | Not offered | Add-on or higher tier | Add-on or higher tier | Not offered | Not offered | Not offered | Not offered | Included |
| Self-hosting option | Not disclosed | Not disclosed | Not disclosed | Included | Not disclosed | Not disclosed | Not disclosed | Not disclosed | Not disclosed |
Capability states come from the sources cited in each profile; most are from [5][16][19].
These come up in the same searches but solve a different problem. Each is sometimes the better answer.
Publish your security posture and answer questionnaires, but don't monitor controls or collect audit evidence.
Right instead when you already hold a SOC 2 report and buyer security reviews are the bottleneck.
Write policies and run readiness work, usually alongside a platform you still pay for.
Right instead when the problem is time, not software. Scytale's own higher packages already include consultants.
Some audit firms include a licence for their own tool with the audit fee.
Right instead when you want one relationship and accept the firm's tool. Check what happens to your data if you change auditor.
Cover risk, policy and audit management across a large organisation, with implementations measured in quarters.
Right instead when you have a dedicated GRC team and many frameworks.
Five steps, in order. Most failed switches skip the first or second.
Download policies, evidence with timestamps, the risk register, vendor reviews and any test history. Some exports are only available while your contract is active.
Switch between observation periods, not during one. If the renewal falls mid-period, ask Scytale for a short extension rather than moving tools mid-audit.
Confirm they can audit from the new platform or accept its exports. If your current audit runs through Scytale's audit line, line up a new firm first.
Connect the new platform and compare its test results with Scytale's for about 30 days before relying on it.
Your auditor may ask for evidence from the old system. Negotiate read-only access, or keep a dated archive of every export.
Answers use the figures on this page. Where a vendor hasn't disclosed something, the answer says so.
On published figures, none is clearly cheaper. Scytale's AWS Marketplace floor is $7,500 a year for the platform and one framework, and Secureframe's Fundamentals package also starts at $7,500. Thoropass's platform starts at $8,700 before its audit. On observed contracts, Sprinto has the lowest median here ($15,000 on Vendr), then Vanta and Secureframe ($20,000). Compare quotes for the same scope.
Not among full managed platforms. Comp AI publishes an AGPLv3 open-core codebase you can self-host, which removes the licence fee but moves operations onto your team; its managed service is quoted on a call.
Thoropass pairs its platform with a related CPA firm, Thoropass Assurance, though software and audit are priced separately. Vanta sells a package that can include an independent auditor's fee, and Comp AI says audits can be included in its quote. Scytale itself sells a third-party audit service from $4,200.
In SOC2Auditors.org's directory, 50 attestation firms list Drata, 45 list Sprinto, 41 list Vanta and 13 list Secureframe. None list Scytale. That matters if you want to choose or change your audit firm without changing tools.
By vendor claims: Comp AI 580+, Vanta 400+, and Drata, Sprinto and Secureframe 300+ each, against Scytale's 150+. Counts are not proof that your own systems produce evidence your auditor accepts, so test the integrations you depend on.
You can, but it is risky during a Type 2 observation period, because your auditor needs continuous evidence for the whole period. Most teams switch between observation periods, or agree in writing with their auditor how evidence from both tools will be accepted.